Are you really audit-ready—or just documented? Most contractors think documentation equals compliance. Here’s how to turn paperwork into real-world security.
So you’ve documented your controls—but do you really know they work?
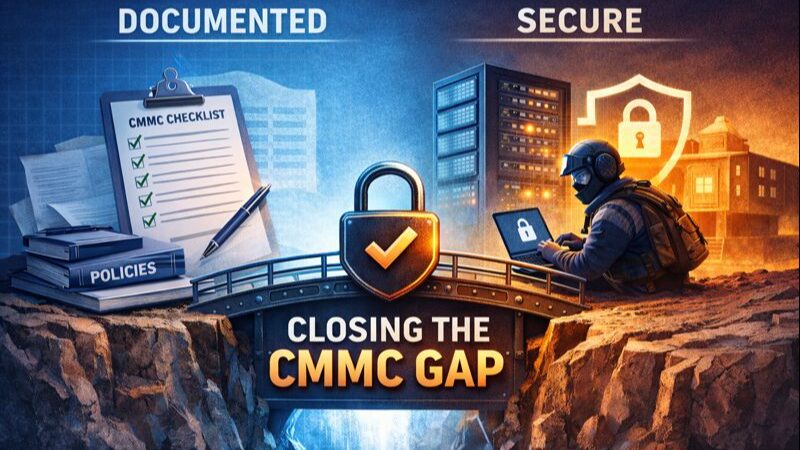
Over the past year, we’ve seen too many defense contractors mistake documentation for security. Policies on paper are a start, but operational compliance—the kind that actually protects Controlled Unclassified Information (CUI)—requires ongoing attention.
Here’s what often trips organizations up:
-
Continuous Validation: Controls aren’t static. Systems, users, and workflows change constantly, so annual checks aren’t enough.
-
Cross-Team Collaboration: Security isn’t just IT’s responsibility. Involving operations, leadership, and project teams early prevents last-minute surprises.
-
Early Assessment Prep: Internal audits can’t fully simulate a C3PAO review. Starting sooner than you think gives you time to address real gaps.
A simple step you can take this month: Pick one critical control—maybe an email system, shared drive, or access process—and run a “live test.” Approach it like an auditor or even a threat actor. You’ll uncover gaps before they become urgent problems.
The reality? Contractors who treat CMMC as a path to real security—not just paperwork—end up stronger and audit-ready.
Where does your organization stand—are you just documenting compliance, or actually living it?